Linux setup

Set up TekLan VPN on Linux

Download a WireGuard or OpenVPN configuration from the Dashboard and use it with your preferred command-line or NetworkManager client.

Setup steps

Choose how to connect

OpenVPN for Linux

Import an OpenVPN profile with OpenVPN 3

These steps match the Linux instructions the Dashboard shows.

Before you begin

  • Confirm OpenVPN 3 Linux supports the distribution and processor architecture.
  • Have an account with permission to install packages.
  • Allow the command-line client to save and import an .ovpn file.

Move the OpenVPN profile to this device

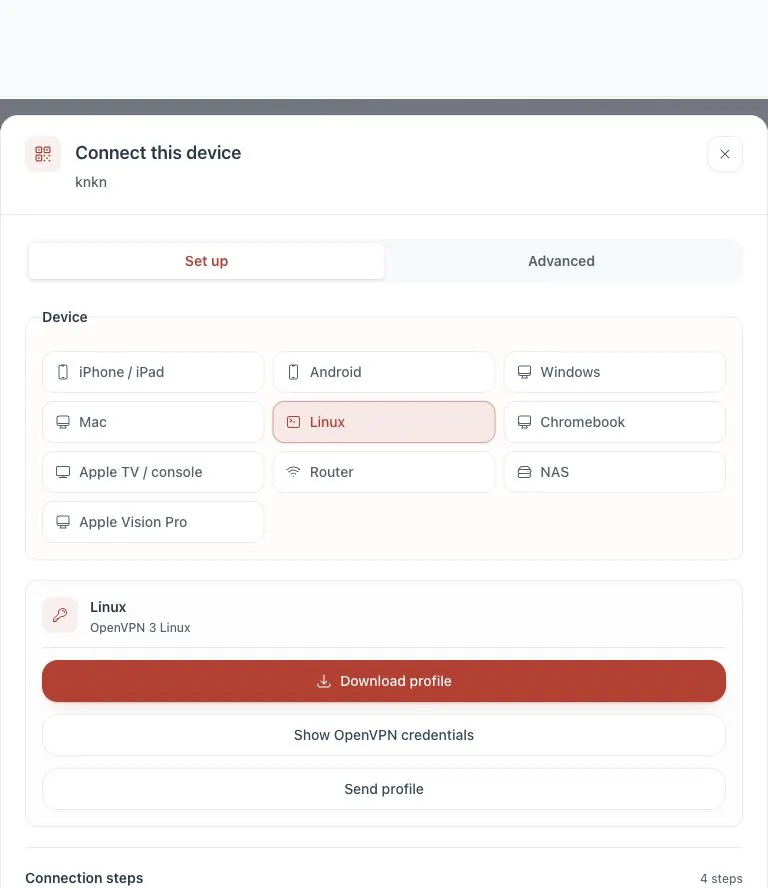
  • Download profile: save the .ovpn file on the device you are setting up.
  • Email: select Send profile, then Send email. The Dashboard sends the .ovpn attachment to your account email address.
  • OpenVPN credentials: select Show OpenVPN credentials and keep the displayed profile username and password available. The password unlocks the private key inside the file. It is not your TekLan VPN password.

Steps

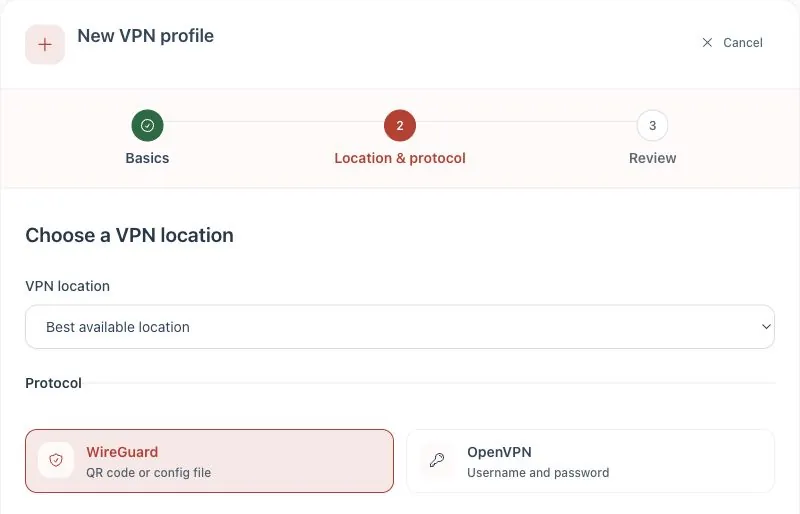
  1. Create an OpenVPN profile in the Dashboard, select Set up this device and choose Linux.
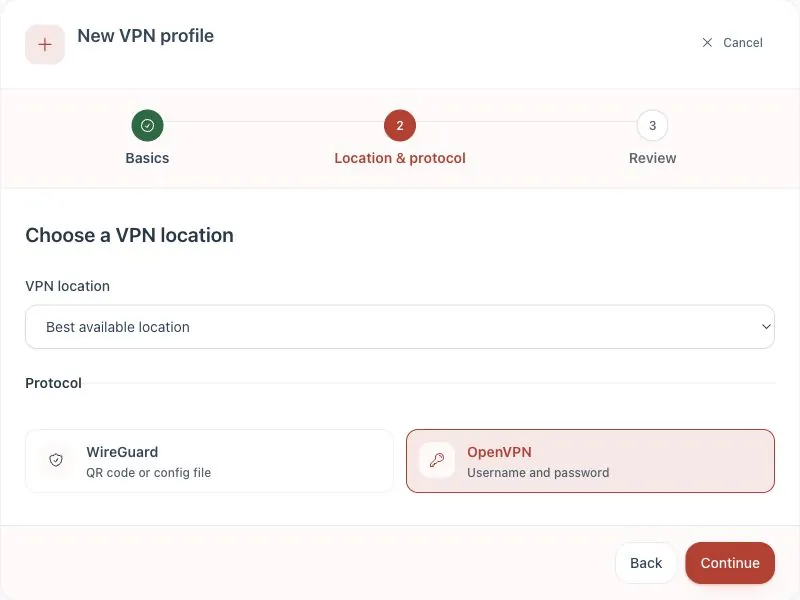
    Selecting OpenVPN
    Choose OpenVPN.
    Linux connection options in the Dashboard
    Choose Linux and use the OpenVPN 3 delivery options.
  2. Install OpenVPN 3 Linux using the instructions for your distribution on openvpn.net.
  3. Download the profile and import it with openvpn3 config-import --config /path/to/profile.ovpn --name TekLan --persistent.
  4. Start it with openvpn3 session-start --config TekLan. If asked for the private-key passphrase, use Show OpenVPN credentials.
  5. Run openvpn3 sessions-list to check the session state.

Check the connection

  1. Run openvpn3 sessions-list and confirm the session is connected.
  2. Open a browser or run an IP check and confirm the public IP address changes.
  3. Disconnect the session and confirm the normal route returns.

If it does not connect

  • Use Show OpenVPN credentials in the Dashboard if the client requests the private-key password.
  • Disconnect another active VPN before retrying.
  • Delete the failed configuration and import a newly downloaded .ovpn file.
  • Read the first error in the OpenVPN 3 session log before opening a support ticket.

Still stuck? See the help articles, or open a support ticket with the exact error you see.
WireGuard for Linux

Import a Dashboard profile on Linux

NetworkManager is the simplest route on most desktop distributions. Use wg-quick on a server or a minimal installation.

Before you begin

  • Install WireGuard and NetworkManager using packages supplied by your Linux distribution.
  • Have permission to add a system network connection.
  • Create a separate Dashboard profile for this computer.

Get the profile on this computer

  • Download: save the .conf file from the Dashboard.
  • Email: use Send profile, then Send email, then save the attachment from your account email.
  • Device code: use Send profile, Get code. Open dash.teklanvpn.com/get, enter the one-use code and download the file within 15 minutes.
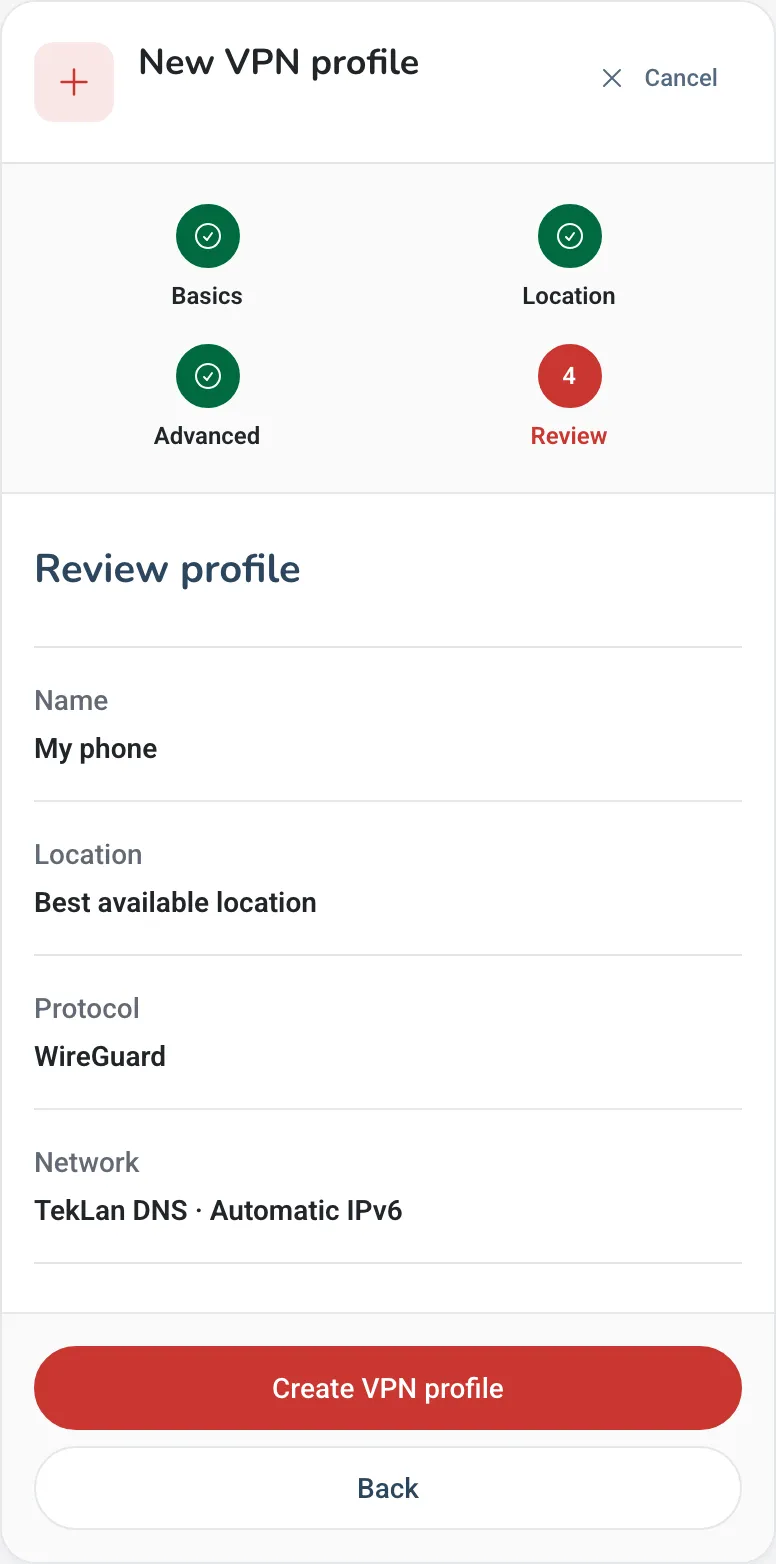
WireGuard profile ready to create in the Dashboard
Review the profile, create it and download the .conf file.

Steps

Connect with NetworkManager

  1. In the client area, open your active VPN service, select Manage VPN Dashboard, then create a WireGuard profile for this computer.
    WireGuard selected while adding a Linux device
    Select WireGuard for this Linux computer.
  2. Open the distribution’s network settings and choose the option to import a VPN or saved connection.
  3. Select the downloaded .conf file, save the connection and switch it on.
  4. If the graphical network settings do not provide an import option, run nmcli connection import type wireguard file ~/Downloads/profile.conf, replacing the path with the real filename.
  5. Use nmcli connection show --active to confirm that the imported connection is active.

Connect with wg-quick

  1. Install wireguard-tools, and openresolv if your system does not use systemd-resolved, so wg-quick can apply the profile’s DNS setting.
  2. Copy the profile to /etc/wireguard/teklan.conf and restrict it with sudo chmod 600 /etc/wireguard/teklan.conf.
  3. Start it with sudo wg-quick up teklan.
  4. Check the tunnel with sudo wg show.
  5. Disconnect later with sudo wg-quick down teklan.

Check the connection

  1. Confirm NetworkManager or wg show reports the tunnel as active.
  2. Open an IP-checking site and confirm the public IP address changes.
  3. Disconnect the tunnel and confirm the normal route returns.

If it does not connect

  • Check that no other VPN connection is active.
  • Confirm the system date, time and DNS resolution are correct.
  • Delete the failed connection and import a newly generated profile.
  • For wg-quick, read the first terminal error and run sudo wg show before opening a support ticket.

Still stuck? See the help articles, or open a support ticket with the exact error you see.